Introduction
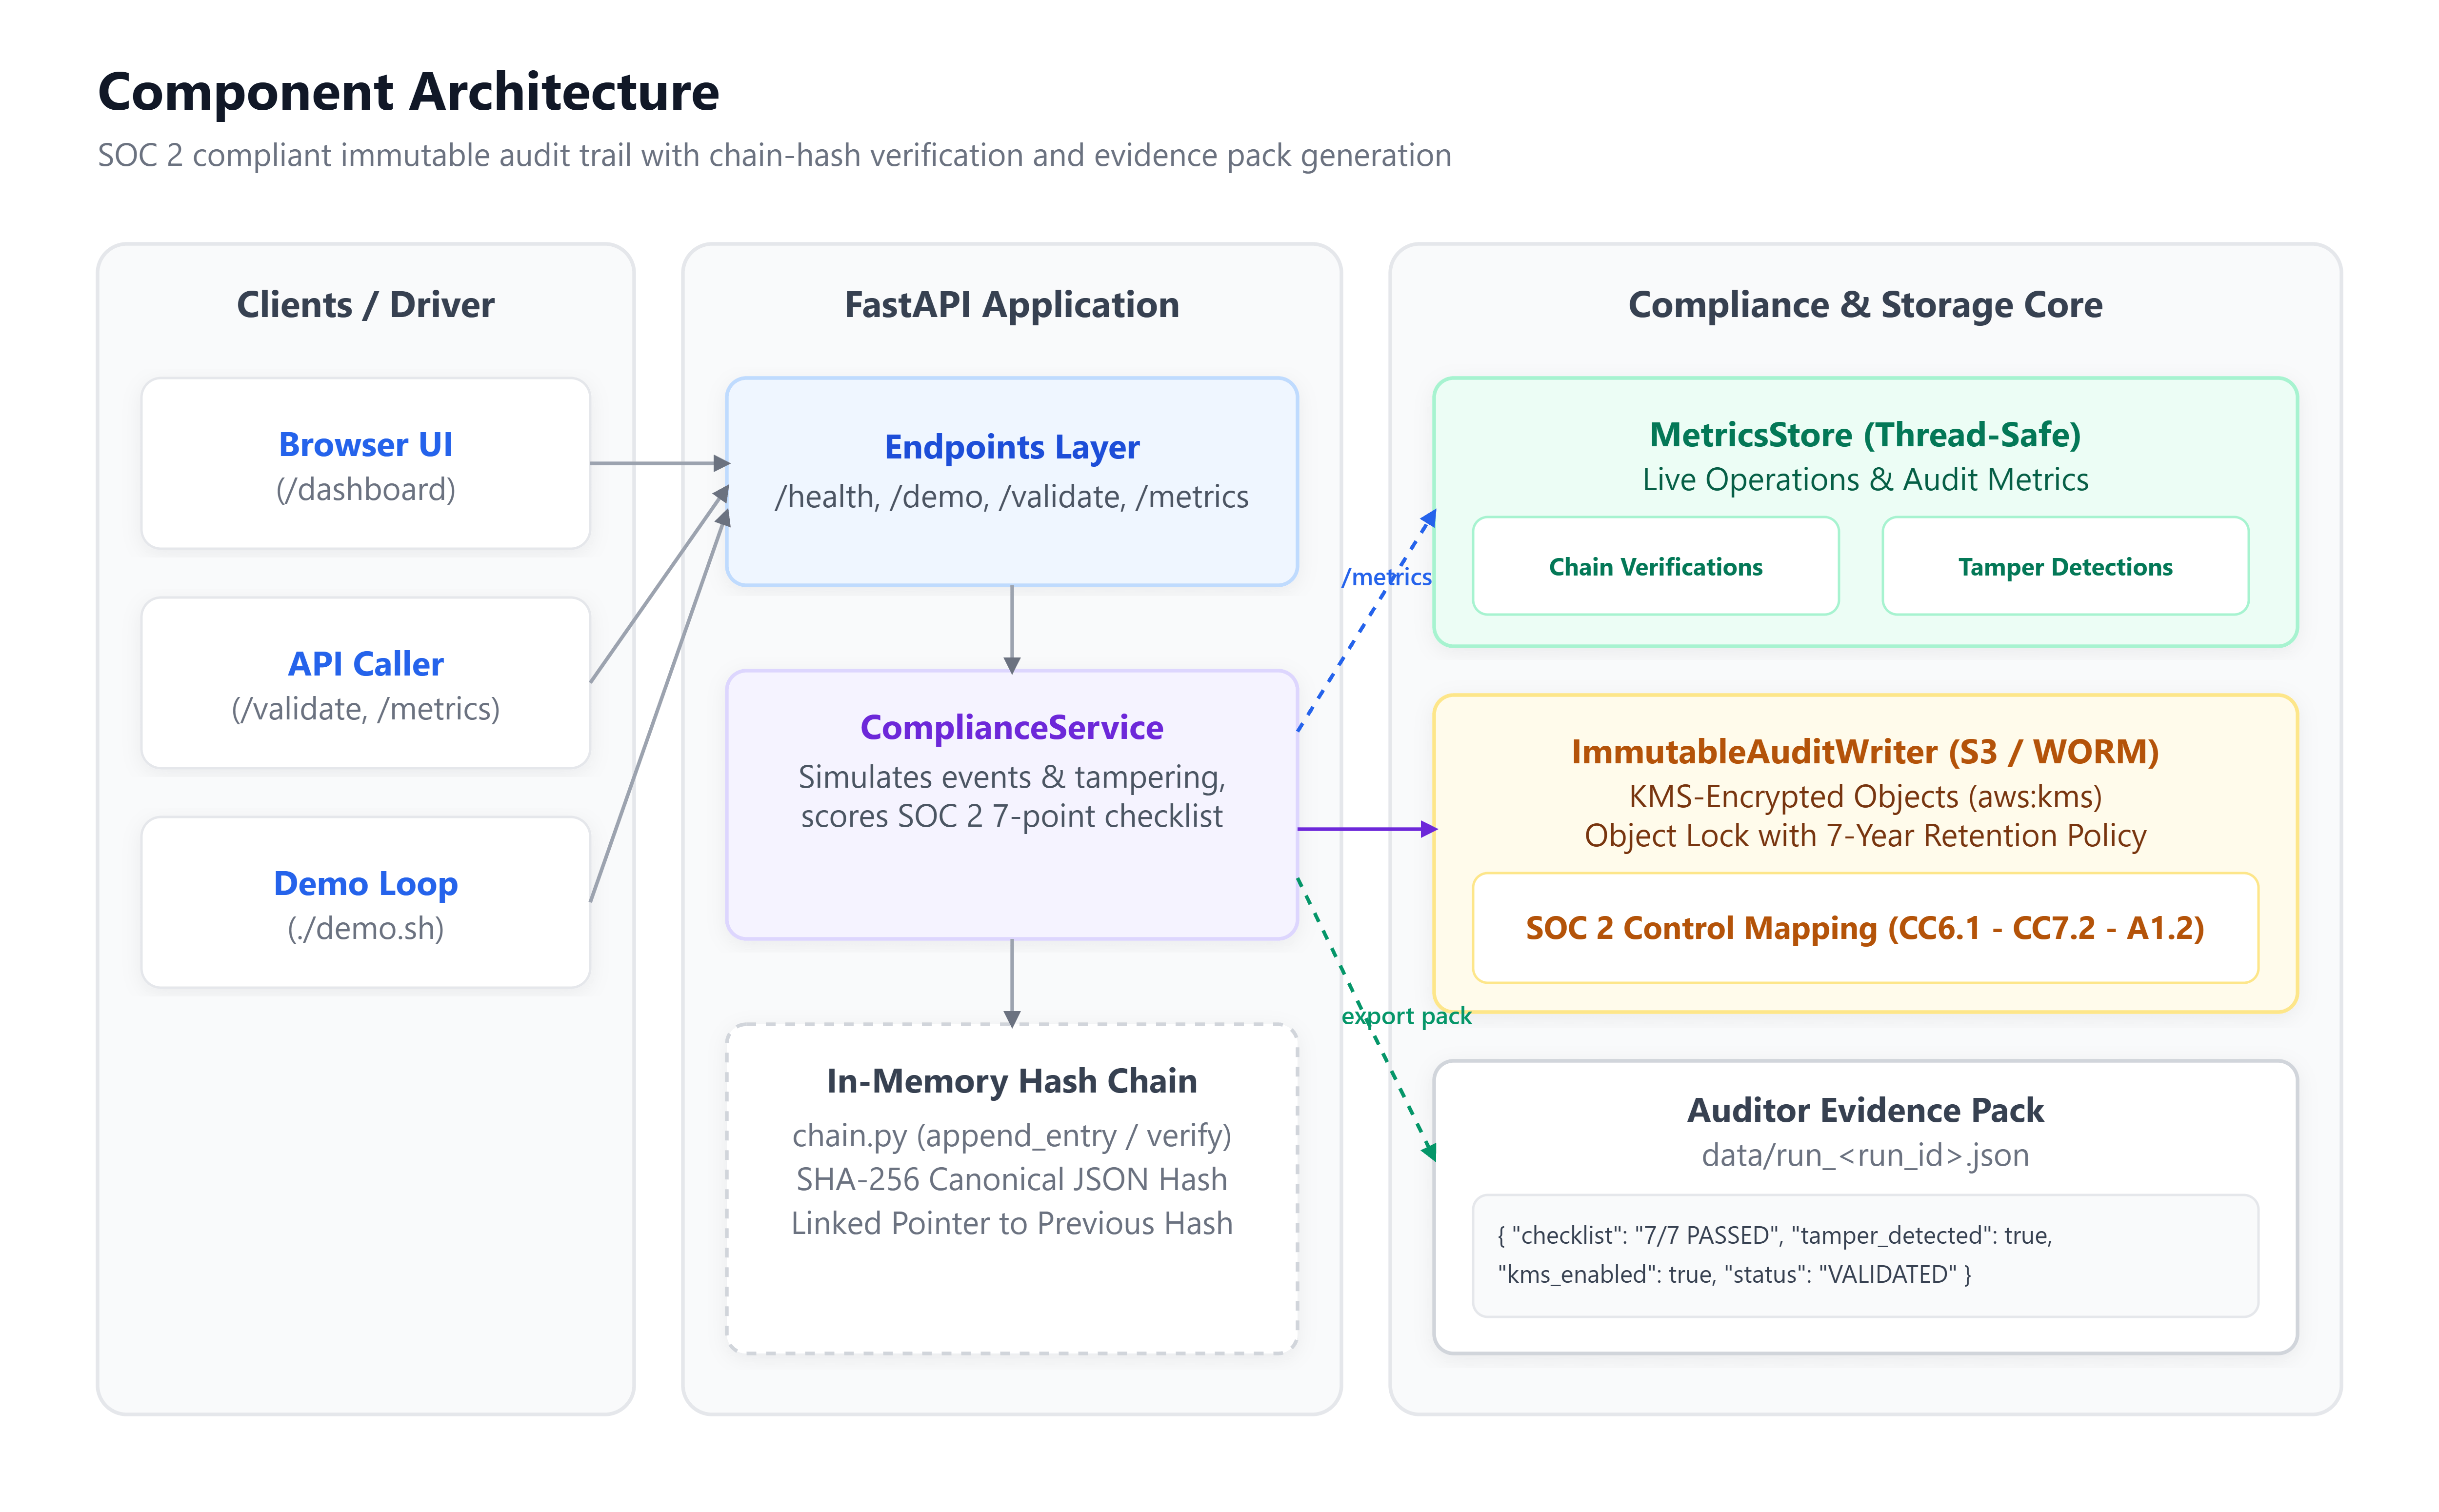
Enterprise AI agents handle sensitive data, invoke external tools, and incur measurable cost. Auditors expect proof that access is controlled, actions are logged immutably, and tampering is detectable. This lesson implements SOC 2–aligned audit trails with chain-hash integrity, RBAC evidence, and an auditor-ready evidence pack. You simulate immutable S3 writes, verify tamper detection on a linked hash chain, and validate seven production controls on a live FastAPI dashboard.
Highlights
Immutable audit entries with SHA-256 chain hashes linking each event to the previous
Content-hash verification detects field-level tampering
SOC 2 control map (CC6.1–A1.2) with evidence URLs
FastAPI dashboard with non-zero metrics after
/demoSelf-contained
aiam-day24on officialpython:3.12-slimvia Docker Compose (port 8124)
What We Build
ImmutableAuditWriterfor KMS-encrypted S3 audit objectsIn-memory
chain.pyfor demo and tests without AWS credentialsComplianceServicesimulating audit trails, tamper detection, and evidence packsFastAPI
/health,/demo,/validate,/metrics,/dashboardScripts:
start.sh,stop.sh,demo.sh,run_tests.sh,cleanup.sh
Connection to Previous Lesson
Day 23 established KEDA autoscaling and FinOps savings. Day 24 adds the compliance layer auditors expect once workloads scale: every agent action must be attributable, retained, and provably unmodified.
Enables Next Lesson
Day 25 (HIPAA-ready agents) builds on immutable logging and access controls. SOC 2 evidence here becomes the foundation for PHI handling and stricter RBAC enforcement.
Architecture Context